Cloud photo storage privacy: who holds the encryption keys?
Written for iPhone and Android owners comparing iCloud Photos, Google Photos, Amazon Photos, Dropbox and OneDrive who want to know who can access their files
Short answer
Every major consumer photo cloud (iCloud Photos, Google Photos, Amazon Photos, Dropbox and Microsoft OneDrive) encrypts your photos in transit and on disk in its data centers. What decides your actual privacy is who holds the decryption keys: in almost all default cloud setups, the cloud company holds the keys so its servers can generate thumbnails, run face/object search and reset forgotten passwords. The two ways to keep decryption keys in your own hands are turning on Apple’s Advanced Data Protection for iCloud, or encrypting your photos on your phone before saving the encrypted backup file to a cloud drive.
On this page
Every mainstream cloud photo service advertises that your pictures are “encrypted in transit and at rest”. That statement is true, and it answers only one half of the privacy question.
Disk encryption in a data center stops a thief who steals a physical hard drive from a server rack. It does not stop the cloud provider itself, an attacker who compromises your cloud login, or a server-side breach from reading your photos, because in standard cloud storage, the provider holds the decryption keys right next to the encrypted files.
Key custody across the 5 major cloud photo services
| Cloud service | Encrypted in transit & at rest? | Who holds the keys by default? | Optional end-to-end encrypted mode? | Server-side AI / face indexing? |
|---|---|---|---|---|
| Apple iCloud Photos (Apple Support 102651) | Yes | Apple (under Standard data protection) | Yes: turn on Advanced Data Protection (where available) | Face & object indexing runs on your device, not on iCloud servers |
| Google Photos (Google Help) | Yes | Google (including backed-up Locked Folder) | No | Runs on Google’s cloud servers |
| Amazon Photos | Yes | Amazon | No | Runs on Amazon’s cloud servers |
| Microsoft OneDrive (incl. Personal Vault) | Yes | Microsoft | No (Personal Vault adds a 2FA identity gate, not client-only E2EE keys) | Runs on Microsoft’s cloud servers |
| Dropbox | Yes | Dropbox | Only on enterprise/business team E2EE add-ons | Runs on Dropbox servers |
Why mainstream photo clouds keep a copy of your key
Cloud photo apps are not keeping keys out of laziness; they do it because three everyday features depend on the server being able to decrypt your images:
- Server-side search and face grouping: when you type “receipt from Tokyo” or “golden retriever” into Google Photos on the web, Google’s servers scan the pixels and OCR text of your photos in the cloud. (Apple is the notable exception here, running People, Pets and visual look-up indexing locally on your iPhone’s Neural Engine rather than in the cloud.)
- Instant web browser galleries: logging into
photos.google.comoronedrive.comfrom a borrowed PC requires the server to render small JPEG thumbnails on the fly. - “Forgot password” account recovery: if you forget your password and the company holds the encryption keys, customer support can verify your phone number or email and hand your library back to you.
How to use any cloud drive without handing over your keys
You do not have to abandon iCloud Drive, Google Drive, Dropbox or OneDrive to get true zero-knowledge encryption. You simply have to encrypt the files on your phone before the cloud drive ever sees them:
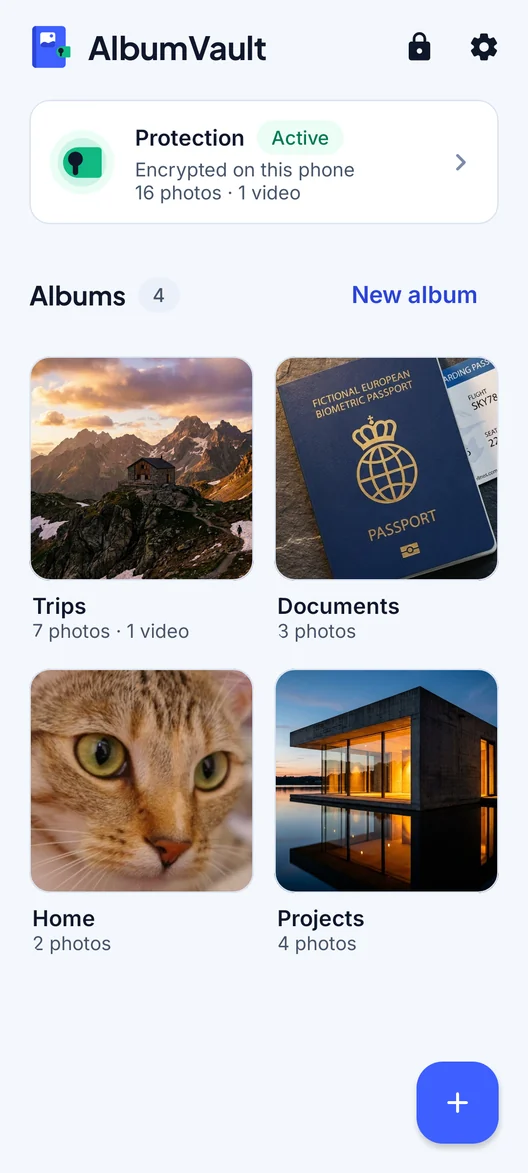
- Move your sensitive photos and videos out of your main camera roll into an on-device encrypted vault app (and delete the originals from Apple Photos / Google Photos plus Recently Deleted / Trash).
- Inside the vault app, export an encrypted backup bundle (where every file and metadata record is encrypted on your phone under a key derived from your 12-word recovery phrase).
- Save that encrypted backup file to Files, iCloud Drive, Google Drive, Dropbox or a USB drive you trust.
- Keep your 12-word recovery phrase written on paper offline, never saved as a screenshot or text file inside the same cloud drive!
With that setup, Google Drive or iCloud Drive provides cheap, redundant off-site storage for your backup file, while seeing nothing more than an opaque block of authenticated ciphertext that only your offline recovery phrase can open.
Questions
Are Google Photos and iCloud Photos encrypted?
Both encrypt your photos in transit (TLS) and at rest on their servers. By default, both companies hold the decryption keys on their servers. Apple lets you switch iCloud Photos to client-held end-to-end encryption by turning on Advanced Data Protection; Google Photos does not offer an end-to-end encrypted mode.
Why do cloud photo services hold my encryption keys by default?
Server-side features like web galleries, automatic face and pet grouping, OCR text search inside images, shared links and email password recovery require the server to read your image pixels, which is only possible if the server holds a decryption key.
Does Google Photos Locked Folder use end-to-end encryption in the cloud?
Google’s Locked Folder documentation states that backed-up Locked Folder items are protected by Google Photos' standard encryption in transit and at rest, and does not claim client-side zero-knowledge encryption.
Is it safe to store an encrypted vault backup file in Google Drive, Dropbox or iCloud Drive?
Yes, provided the vault app encrypted the backup bundle on your phone before you uploaded it using a strong key or 12-word recovery phrase that you never store inside that same cloud account.
What happens if I lose my password on a zero-knowledge encrypted backup?
Because the cloud provider never holds your decryption key, customer support cannot unlock an end-to-end encrypted backup for you. Always keep your recovery phrase written down offline.
Keep reading
Are iCloud Photos encrypted?
Yes, but by default Apple holds the keys. Advanced Data Protection makes Photos end-to-end encrypted, with a few exceptions.
GuideWhat is zero-knowledge encryption?
Your data is encrypted on your own device with a key the service never gets. It is strong, but nobody can reset your password for you.
GuideCan Apple see your hidden photos on iPhone?
By default, iCloud uses Standard data protection where Apple holds the keys. Here is how Advanced Data Protection and local vaults change that.